Control short-lived virtual machines!
Adordis enables you to quickly launch customizable virtual machines to execute isolated and potentially unsafe activities.
Actions can either be fully automated, e.g., converting PDFs or running any program, or controlled graphically by the user, e.g., to open an Excel file with macros in an isolated environment.
Adordis Shield for your Cyber Security
Adordis Shield enables use cases for content disarm & reconstruction as well as use cases for opening potentially harmful files in an isolated and graphical environment.
You can spin up pre-booted virtual machines with a graphical user interface to, for example, open and edit third-party office files that contain macros. Each time, a completely new virtual machine is launched. [more]
Content Disarm & Reconstruction
In contrast to traditional virus scanning solutions, the approach of Content Disarm & Reconstruction (CDR) protects against known threats and against unknown threats in files by removing executable or malicious content. This is often achieved by converting the content or by using a whitelist of safe elements, depending on the file type.
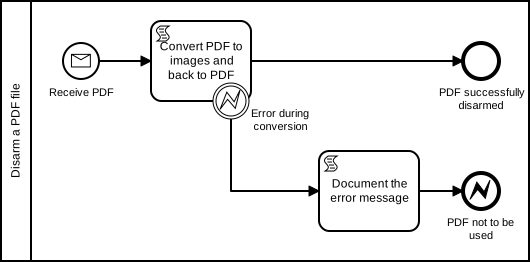
This example illustrates the basic approach in Adordis Shield and an implementation stripped of details. Script tasks in BPMN control the startup of a virtual machine (VM) with form data (Message Start Event). Here, a VM would receive the uploaded PDF file and execute a custom script in an isolated environment to convert it to images and back to a PDF. If OCR is part of the script, the converted PDF file will remain searchable.
Isolation based on virtual machines significantly reduces attack vectors: Malicious files can still exploit software vulnerabilities, but lack the ability to cause significant harm without internet or network access, or access to other confidential information. Moreover, no state is carried over to future instances, i.e., virtual machines are used once and their state vanishes.
This approach is similar to printing and scanning documents on a computer that has been used only once for this purpose only. Moreover, the approach of capturing visible parts of a document ensures that redacted sections cannot be unveiled.
Isolated remote desktops
If potentially dangerous files need to be opened and used interactively, virtual machines (VMs) with a graphical user interface are suitable for one-time use. This way, preconfigured VMs with the necessary software can be launched once, incoming files can be opened in this isolated environment, and output files can be exported.
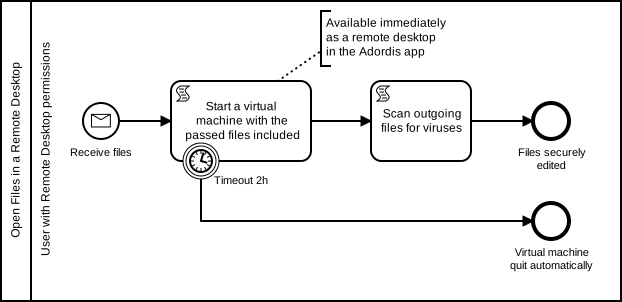
This example illustrates how to launch a graphical user interface in conjunction with a virus scan of output files in a subsequent virtual machine. If necessary, e.g., to comply with requirements from your customers or suppliers, you can open Excel files containing macros or fill out potentially harmful PDF forms.
The basic approach of Adordis Shield is customizability via process models. This way, you are free to implement and apply your own approval processes - for example in order to provide time-limited, virtual desktops for remote maintenance with access to a specific internal network. Moreover, the approach enables access to shared software licences for a short time-period.
Users of virtual machines are only required to have a web browser - and do not need to install any additional software. The remote desktop is provided by the hypervisor and operates independently of whether the virtual machine is granted network access.
Advantages